- Support
Submit a ticket - Help Center
- Partner
Become a Partner - Learn
Blog - What's New
- FAQs
- Support
From the day someone joins to the day they leave, inLynk Crew governs attendance, leave, timesheets, policies, and access from one permission-scoped workspace — with a full audit trail on every step in between.
96.4%
Attendance this week
12
Pending approvals
Trusted by fast-growing teams worldwide


Every stage of employment runs through the same governed workspace — nothing to reconcile between separate tools.
A reusable checklist — laptop, email, access cards, documents — instantiated the moment a new hire joins.
7 capabilitiesCheck in, apply for leave, and see requests move through manager approval, all against the same record.
22 capabilitiesTime logged against real projects, submitted, and approved — with every request landing in one shared inbox.
15 capabilitiesPolicies, documents, compensation, and career growth — a self-service helpdesk employees actually use.
24 capabilitiesClearance, asset return, access removal, and exit interviews — connected end to end, nothing left stuck.
7 capabilitiesNine of the twenty modules inside inLynk Crew — permission-scoped, and configured to match how your organization already works.
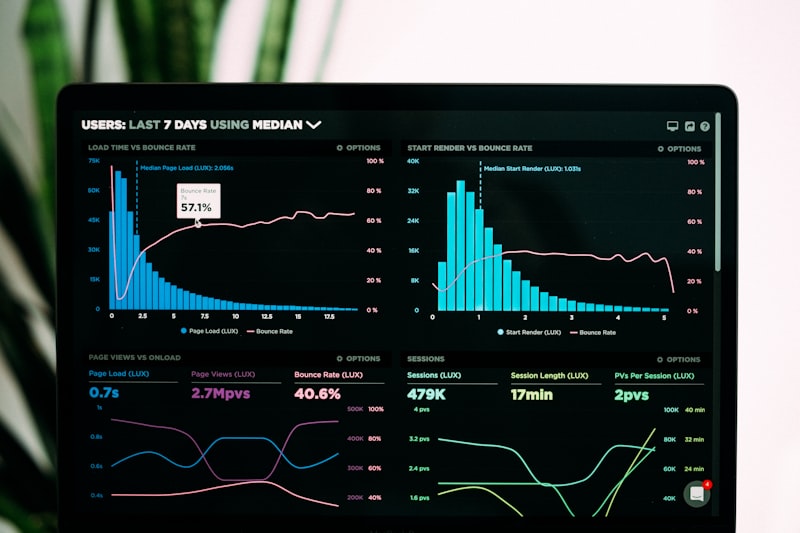
Profile card, live clock, check-in/check-out, and a daily summary right after login.
Apply for leave, track balances and holidays, and see approvals move in real time.

Working hours, regularization, on-duty requests, and team attendance in one view.

A self-service HR helpdesk for documents, policies, compensation, and career growth.
Every employee's own profile record, kept current and visible only to the right people.
Company policies, handbooks, and announcements, with acknowledgement tracked automatically.

Reusable new-hire checklists instantiated per employee — nothing left to remember manually.

Clearance, asset return, access removal, and exit interviews, connected end to end.

A searchable record of who did what, to which record, when, and from which IP address.
Access control and audit are enforced on every request, not just shown in the interface.
System roles — member, admin, and super_admin — plus unlimited custom roles, each scoped to exactly the permissions they need.
Sidebar and page access follow the same permission set on both the frontend and the backend — nothing is hidden by the interface alone.
Restrict access to approved network ranges, with correct handling of reverse proxies, trusted headers, IPv4/IPv6, and VPN scenarios.
Every sensitive write — approvals, permission changes, policy acknowledgements, configuration edits — is logged with actor, IP, and timestamp.
Modules across the platform
Individual capabilities
Configuration areas per organization
Server-side permission checks
Tell us about your HR team and requirements — one module or the full platform — and we'll get back to you.
Twenty modules, permission-driven access, and a full audit trail — configured to match how your organization already runs HR.